
The Independent Review of the Security of Critical Infrastructure Act 2018 has delivered a clear mandate: mandatory cyber threat intelligence sharing, bidirectional government–industry exchange, and a fundamental shift from compliance culture to proactive security. CI-ISAC Australia is positioned to deliver it.
Key Findings of the Slay Review — and Why They Matter
Dr Jill Slay AM’s Independent Review of the Security of Critical Infrastructure Act 2018 is the most significant policy signal Australia has produced on cyber threat intelligence (CTI) sharing. Conducted across 600+ roundtable participants in the Trusted Information Sharing Network (TISN), the review’s verdict was direct: the Act is too reactive and too slow relative to the pace of evolving threats.
Key findings include:
- 70% of stakeholder sentiment about the SOCI Act was negative — not about its intent, but its inability to keep pace with nation-state actors, AI-enabled attacks, and supply chain compromises that have transformed the threat landscape since 2018.
- Majority support for mandatory CTI sharing — Mentimeter polling across 460+ town hall attendees confirmed that critical infrastructure operators favour mandatory over incentivised cyber threat intelligence sharing across all sectors.
- A compliance culture without conviction — Practitioners are focused on attestation cycles and audit readiness rather than the adversary, the threat, and the consequences of failure. Legislation can mandate sharing; it cannot mandate the conviction that makes sharing meaningful.
- Recommendation 5 calls for mandatory cyber threat intelligence sharing across all regulated sectors, with education, benchmarking, and structured cross-sector exercises as critical enablers.
- Recommendation 6A mandates bidirectional government–industry intelligence exchange — requiring two-way threat information flow between government and operators, modelled on the US CISA framework.
- The Government has accepted all six recommendations in principle. Reform is underway, and Tranche 2 consultation — where the institutional architecture for mandatory sharing will be determined — is the critical window.
CI-ISAC Australia: The Existing National Capability
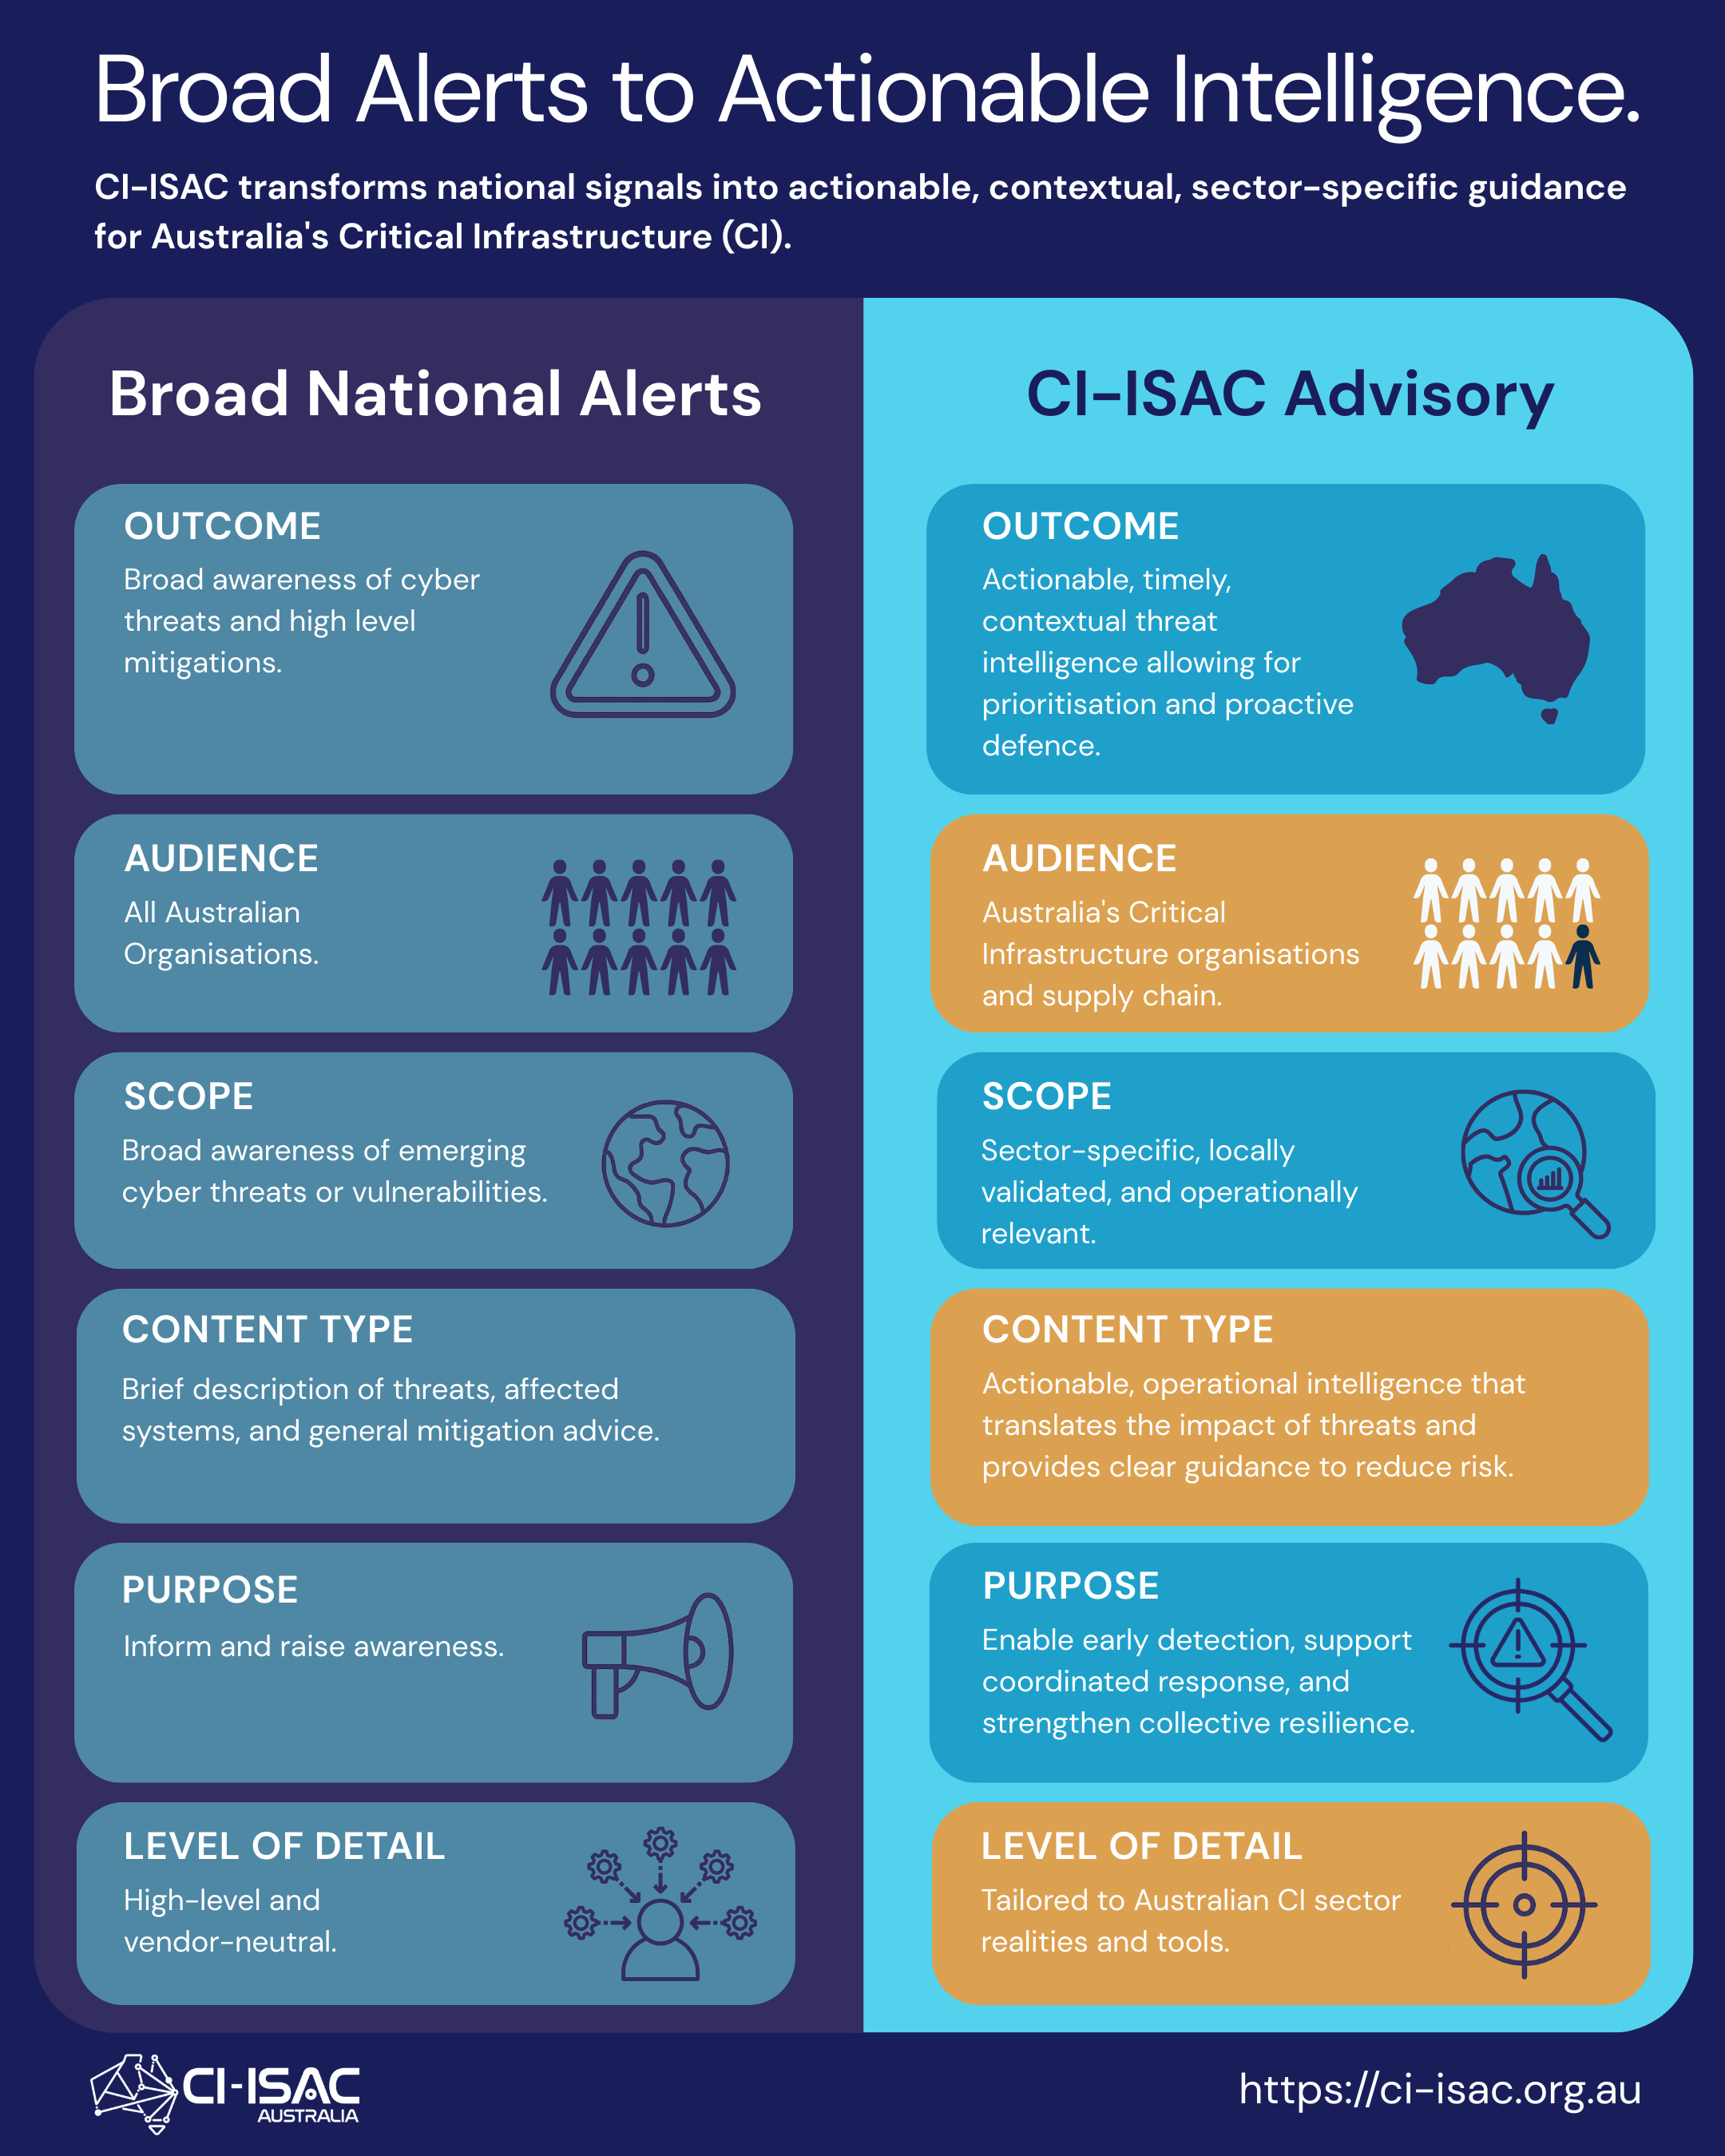
CI-ISAC Australia is the nation’s only cross-sector, not-for-profit cyber intelligence sharing organisation. We are not a proposal or a pilot — we are an active, operating network delivering threat advisories, vulnerability feeds, MITRE ATT&CK-mapped intelligence, and real-time situational awareness to critical infrastructure operators every day.
The reform process should mandate and resource what already exists — not replicate it through a new mechanism that carries the fragility it is designed to avoid.
The Health Cyber Sharing Network proves the model at scale.
Commissioned by the Department of Home Affairs to test whether the health sector warranted a dedicated intelligence capability, CI-ISAC delivered. Health is now our largest sector: 60+ member organisations spanning 600+ facilities — hospitals, pathology providers, digital health infrastructure, aged care, and the medical supply chain — operationalised in under a year. The Health Cyber Sharing Network is the template for how Recommendations 5 and 6A get implemented across every regulated sector.
What we are calling for:
- Mandate participation in CI-ISAC’s cross-sector intelligence network as the delivery mechanism for Recommendations 5 and 6A — not a new government-built structure that replicates what already exists.
- Formalise bidirectional exchange through CI-ISAC’s platform: government and cross-sector sightings in, actionable intelligence out across all critical infrastructure sectors.
- Credit participation in enforcement decisions, as proposed in Recommendation 6A. Operators engaged with the network should carry demonstrable regulatory advantage under the incoming penalty regime.
The Window to Shape Reform is Open Now
Tranche 1 consultation closes 1 May 2026. Tranche 2 — where the information sharing mandate and legislative architecture will be determined — opens soon after. The drafting is where the detail and the risk live.
For critical infrastructure operators, the question is no longer whether these changes are coming. It is how they will be operationalised — and whether your organisation is positioned to benefit from the regulatory credit proposed under the new enforcement regime.
Operators should act now:
Review your current information sharing arrangements against the Part 4 SOCI framework. Understand what you are legally permitted to share, and where genuine ambiguity exists versus perceived risk. Participation in cross-sector intelligence sharing reduces the cost of meeting CIRMP obligations — and may carry direct regulatory credit under the incoming enforcement regime.
For health sector operators specifically: consider what the proposed redefinition of Healthcare and Medical asset classes means for your obligations, your supply chain security posture, and your intelligence gaps.
Request a briefing to discuss CI-ISAC membership and how your organisation can secure the regulatory credit proposed in the reforms.
Read CI-ISAC’s Full Analysis
Policy Commentary: The SOCI Act Review and the Case for Mandatory Intelligence Sharing [View PDF]
An eight-page analysis of the review’s findings, what they mean for operators across all regulated sectors, and CI-ISAC’s perspective on the reform task ahead. Covers CTI literacy gaps, cross-sector risk, the legal barriers to sharing, and what genuine sovereign capability looks like.
CI-ISAC Australia | April 2026 | TLP:WHITE
CI-ISAC Position Statement on the SOCI Act Review [View PDF]
A two-page summary of CI-ISAC’s response to the review — what was found, what CI-ISAC is calling for, and how operators can act now.
CI-ISAC Australia | April 2026
About CI-ISAC Australia
CI-ISAC Australia is a not-for-profit cyber intelligence sharing organisation. We operationalise threat intelligence for our members — translating raw vulnerability data, adversary behaviour, and sector-specific incident reporting into actionable guidance at the speed the threat environment demands. Our membership spans Australia’s largest finance, health, energy, and telecommunications providers, as well as federal, state, territory, and local government. We are an active participant in Australia’s TISN community and a public submitter to the Independent Review of the SOCI Act 2018.
#leavenoonebehind —www.ci-isac.org.au